What "AI Agent Integration" Actually Means
An AI agent, in this context, is software that can perceive information (from a CRM, ERP, email, or database), reason about it using a language model, and take action — creating a record, updating a field, sending a message, or triggering a workflow — with minimal or no human intervention at each step.
Integrating an agent with your business applications means giving it:
- Read access to relevant data (customer history, inventory levels, open invoices)
- Write access to take approved actions (create a lead, update a stock count, generate a purchase order)
- Context about business rules, so its actions stay within policy
- Guardrails that define what it can do autonomously versus what needs human approval
This is meaningfully different from a traditional system-to-system integration, where data simply flows from Point A to Point B on a fixed schedule or trigger. An agent makes decisions along the way — which means the integration has to account for judgment, not just data transfer.
Integration Architectures: Choosing the Right Approach
There are three broad patterns for connecting AI agents to CRM, ERP, and business applications, and most mature deployments end up using a mix.
1. Native or Vendor-Provided AI Connectors
Many major CRM and ERP platforms (Salesforce, Microsoft Dynamics, SAP, NetSuite) now ship native AI agent frameworks or copilots that connect directly to their own data models. This is the lowest-friction path if you're staying within a single vendor ecosystem — permissions, data structures, and audit trails are already built in.
The tradeoff: native agents are usually confined to that vendor's platform. If your agent needs to act across CRM and ERP and a separate support tool, native connectors alone won't get you there.
2. API-Based Custom Integration
This is the most flexible and most common approach for cross-system agents. The agent connects to each application's REST or GraphQL API, using the same authentication and permission model a human integration would use (OAuth, API keys, service accounts).
Best practices here mirror standard API integration hygiene:
- Use scoped API tokens with least-privilege access, not admin-level credentials
- Rate-limit and queue agent-initiated calls to avoid overwhelming source systems
- Log every agent action with the same audit detail as a human user action
- Version your API contracts so agent behavior doesn't silently break on a system update
3. Middleware and Agent Orchestration Layers
For organizations connecting agents to many systems at once, an integration or orchestration layer (iPaaS platforms, or newer agent-specific protocols like MCP — Model Context Protocol) sits between the AI agent and each business application. The agent talks to one consistent interface; the middleware handles translation to each system's specific API.
This pattern scales better as your application landscape grows, and it centralizes governance — you define access rules once, in the middleware, rather than replicating them inside every agent.
Data Governance and Security: The Non-Negotiables
Connecting an AI agent to systems of record raises the stakes on governance considerably, because the agent isn't just reading data — it can act on it.
- Least-privilege access. Give agents the narrowest scope of data and actions needed for their specific task. A sales-qualification agent shouldn't have write access to your general ledger.
- Human-in-the-loop checkpoints. Define which actions an agent can complete autonomously (updating a contact's phone number) versus which require approval (issuing a refund, changing a credit limit).
- Full audit logging. Every agent action should be traceable — what it read, what it decided, what it changed, and why, ideally with the reasoning captured for review.
- Data residency and privacy compliance. If the agent uses a third-party LLM, confirm what data leaves your environment, where it's processed, and whether it's retained or used for model training.
- Rollback capability. Agents will occasionally act on incomplete or ambiguous context. Build in the ability to reverse or flag actions quickly, the same way you would for a human data-entry error.
This is where the discipline overlaps with something IT and finance teams already know well from ERP data management: configuration over customization. Wherever possible, use your CRM or ERP's built-in permission and workflow structures to govern agent behavior, rather than writing custom logic that bypasses those controls.
Step-by-Step: Integrating an AI Agent With CRM and ERP
- Define the use case narrowly. Start with one clear, bounded task — "qualify inbound leads and update CRM status," not "manage all sales operations."
- Map the data and actions required. List exactly which fields, records, and API endpoints the agent needs to read and write.
- Choose the integration pattern. Native connector, API-based, or middleware — based on how many systems the agent needs to touch.
- Set permission boundaries. Configure scoped credentials and define autonomous-vs-approval actions before the agent goes live.
- Build in observability. Set up logging, alerting, and a dashboard so a human can monitor agent activity in real time.
- Pilot with a subset of records or a single branch/team. Validate accuracy and behavior before rolling out company-wide.
- Establish a feedback loop. Route agent errors or edge cases back to whoever owns the prompt, rules, or integration logic for continuous tuning.
Common Pitfalls
- Over-scoping the first project. Trying to automate an entire sales or procurement process at once, instead of one well-defined task, is the fastest way to lose trust in the system after the first visible mistake.
- Treating the agent like a static integration. Unlike a fixed data sync, an agent's behavior can drift as prompts, models, or source data change — it needs ongoing monitoring, not a one-time setup.
- Skipping the audit trail. Without detailed logging, a single incorrect agent action can be impossible to trace back and explain to auditors or customers.
- Granting broad, standing access "to be safe." This inverts the security model — agents should request and be granted access as narrowly as the task allows.
- Ignoring system rate limits. Agents can generate far more API calls than a human user would in the same period, which can throttle or destabilize source systems if not managed.
Real-World Example: Northbridge Manufacturing
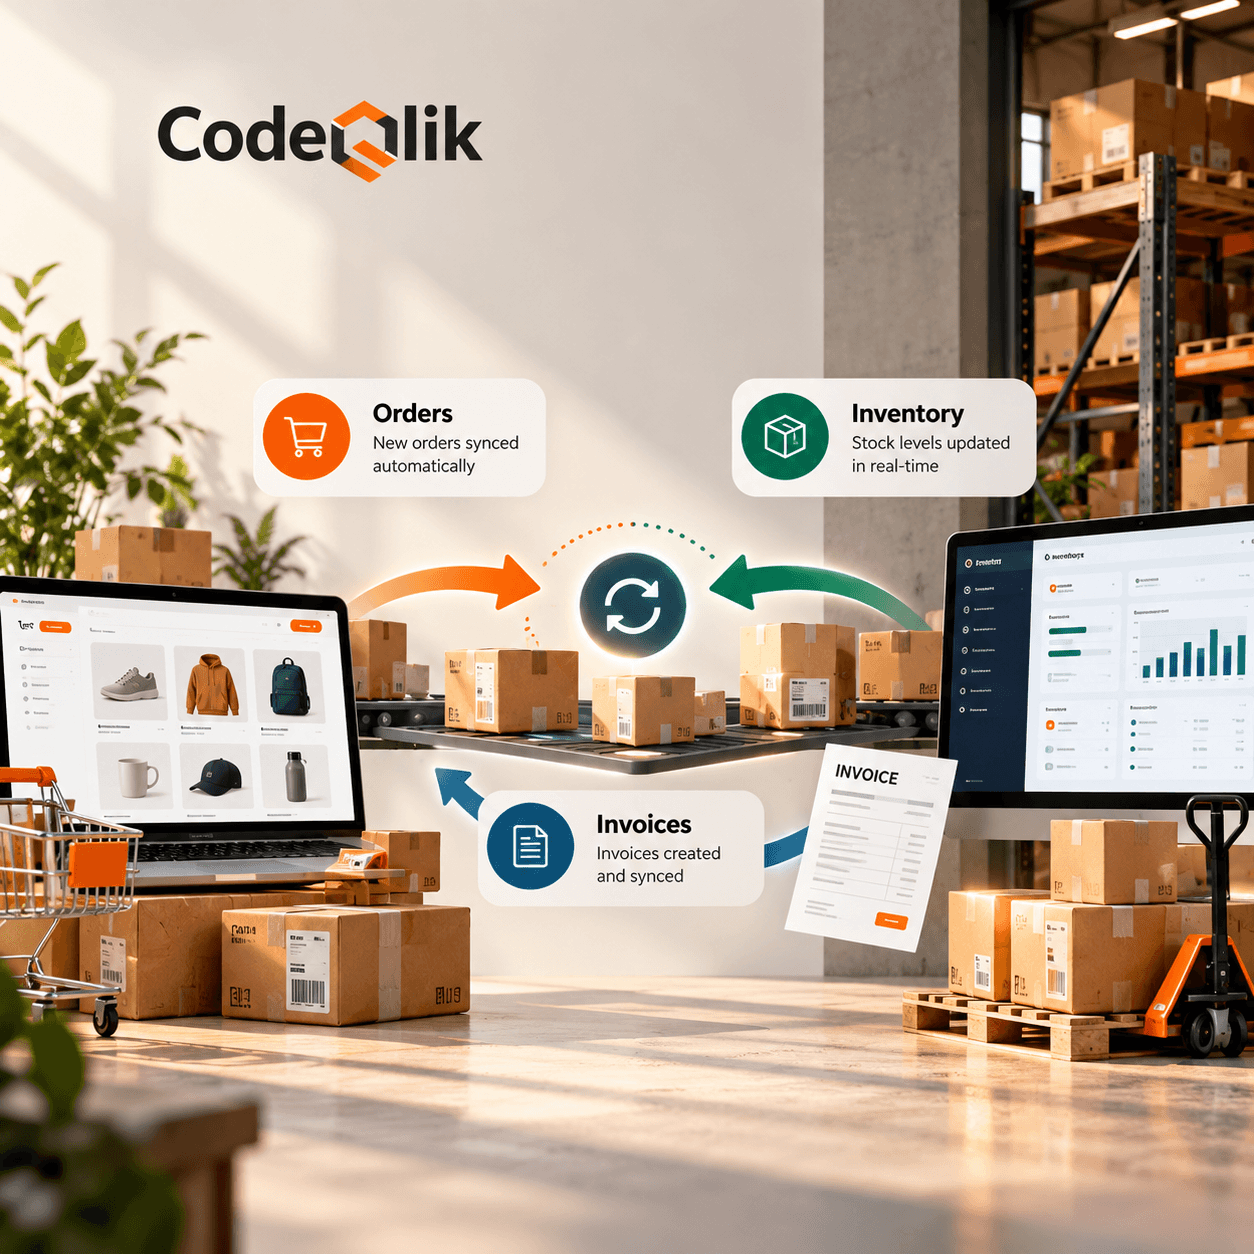
Northbridge Manufacturing (a composite, illustrative example) wanted to reduce the time its sales team spent manually checking ERP inventory before confirming CRM quotes. Rather than building a broad "sales assistant" agent, they scoped a single agent to one task: when a quote reached "pending confirmation" in the CRM, the agent would check real-time stock and lead times in the ERP, then either confirm the quote automatically or flag it for a rep if inventory was insufficient.
The integration used API-based access with read-only ERP permissions and write access limited to a single CRM status field. Every agent decision was logged with the inventory data it used. Within the first quarter, quote confirmation time dropped from an average of six hours to under ten minutes, with a 2% exception rate — all flagged correctly for human review rather than acted on incorrectly.
Implementation Checklist
Planning
- Define one narrow, well-bounded use case
- Map required data fields and actions across systems
- Choose integration architecture (native, API-based, or middleware)
Security and governance
- Configure least-privilege, scoped credentials
- Define autonomous vs. human-approval action boundaries
- Set up full audit logging for every agent action
Rollout
- Pilot with a limited data set or team before full deployment
- Monitor performance, exception rate, and accuracy closely in week one
- Establish a feedback loop to tune prompts, rules, and permissions
Ongoing operations
- Review audit logs and exception cases on a regular cadence
- Reassess agent scope as trust and accuracy improve
- Revisit API rate limits and system load as agent usage scales
The Bottom Line
AI agents can genuinely transform how CRM, ERP, and business applications work together — but only when the integration is treated with the same rigor as any enterprise system connection, plus the added discipline of permission boundaries and human oversight. Start narrow, secure the access model first, and expand scope only as accuracy and trust are proven out.
Want a clearer picture of where AI agents fit in your own systems? Download our whitepaper on enterprise AI agent architecture, or contact our team to schedule a no-obligation AI integration readiness assessment.
Loading comments...